Connector
OPC DA
To configure the connector to the FactoryTalk Linx OPC DA server, from the Project Explorer select Connect, Connectors.
Click Add
Select Rockwell Automation, FactoryTalk Linx Gateway Real-time values (OPC DA)
Click OK
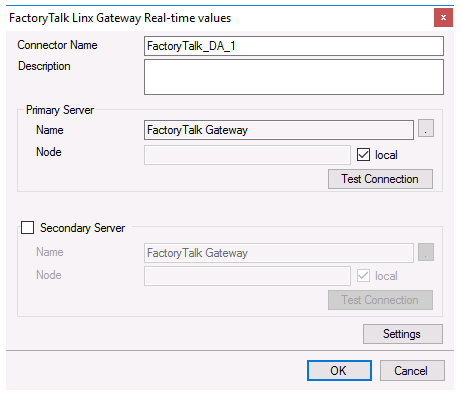 |
Primary Server
These settings define the Name and Node of the OPC DA server. Typically, the Name is defaulted correctly. If the FactoryTalk Gateway server is on the local machine, leave local checked. Otherwise, uncheck and specify either the name or IP address of the machine where FactoryTalk Linx Gateway is running.
Use the Test Connection button to verify a connection to the server.
Secondary Server
These settings define the (optional) secondary FactoryTalk Linx Gateway to connect to if a connection to the Primary Server fails.
Settings
For information on the specific settings, see the OPC Connectors document.
OPC UA
To configure the connector to the FactoryTalk Linx OPC UA server, from the Project Explorer select Connect, Connectors.
Click Add
Select Rockwell Automation, FactoryTalk Linx Gateway Real-time values (OPC UA)
Click OK
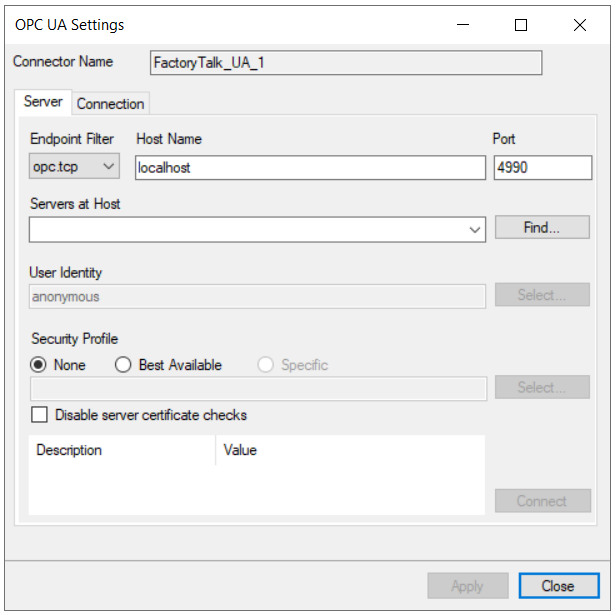 |
Under the Server tab, for Host Name, select or enter the name or IP address of the machine where the server is running. For Port specify the Port as configured in the FactoryTalk Administration Console, OPC, UA Server Endpoints settings.
For Servers at Host click Find and then choose FactoryTalkLinxGateway.
For User Identity click Select to specify
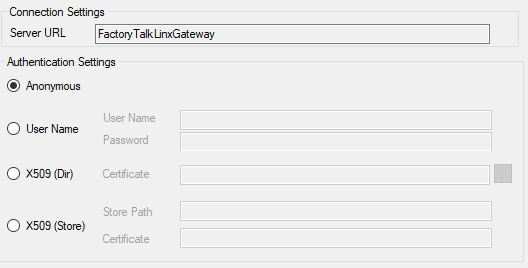 |
If in the FactoryTalk Administration Console, the UA Server Endpoints configuration has Anonymous checked under the Authentication Settings, Anonymous can be selected here. If FactoryTalk Security User is checked (and Anonymous is not), User Name must be selected here and specified as a valid FactoryTalk user.
Security Profile defines the endpoint to connect to for the FactoryTalk Linx OPC UA Server. Select the profile that matches the Security set in the UA Server Endpoints in the FactoryTalk Administration Console. To use a specific endpoint, select Specific and click the Select button.
Click Get Endpoints to get the list of available endpoints, select the one that best fits with the server settings and click OK.
Click Connect to ensure connectivity. This may require an exchange of certificates between the client and the server. If prompted to exchange, click Yes. This action requires Windows administrator rights.
If the Connect fails, be sure that the client certificate is trusted by the server and then attempt to Connect again. For more information, see the Trusted Clients section below.
The Disable server certificate checks option can be used to bypass all the checks normally done against the certifcate passed back from the OPC UA server. This is typically used if settings like the Domain or Application URI do not match what is expected but you would like to proceed with connection. Use this setting with caution as it disables many security features.
Under the Connection tab are Certificate options and general Settings.
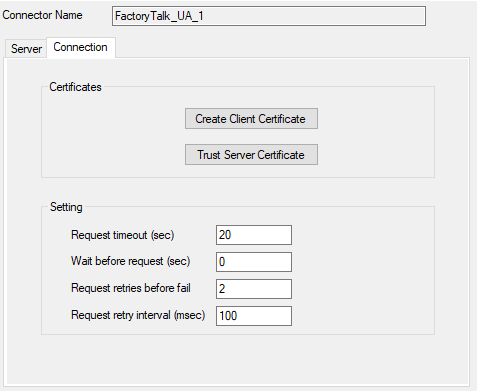 |
The Client Certificate is automatically created on installation. If required, to recreate the certificate select Create Client Certificate. For most OPC UA servers, the default settings will be sufficient, but if the server requires more advanced certificate settings you can specify them with the Advanced button. Click Create to creating the client certificate.
Trusted Clients
In some cases, the client must be accepted by the server to make requests. From within the FactoryTalk Administration Console, OPC select Certificate Management.
Under the Incoming Certificate tab, if the client certificate is listed under Rejected Certificates, select it, and click Trust.